Login-walled
Cops Can Bypass iPhone’s Automatic Reboot to Get Into Locked Phones, Leaked Video Claims
Lorenzo Franceschi-Bicchierai
6 - 7 minutes
A company that makes phone hacking devices claims to have developed a solution that freezes iPhones in a state that lets cops more easily access sensitive data inside them, according to a video obtained by 404 Media.
This is the latest salvo in the never-ending battle between Apple and companies that help cops — sometimes those in authoritarian countries — break into iPhones.
In November 2024, 404 Media revealed Apple quietly introduced a new feature in iOS that automatically reboots an iPhone that has not been unlocked for 72 hours. The idea behind this so-called “inactivity reboot” is to revert the phone to a state that makes it harder for police to break into the device, and thus extract sensitive data from it with forensics technology.
At the time of Apple’s change, law enforcement agents expressed concern about this new feature, given that oftentimes they can’t immediately try to break into iPhones that have been seized. That could be because police are still waiting for a court authorization to do so, or there is simply a backlog of devices to unlock, for example.
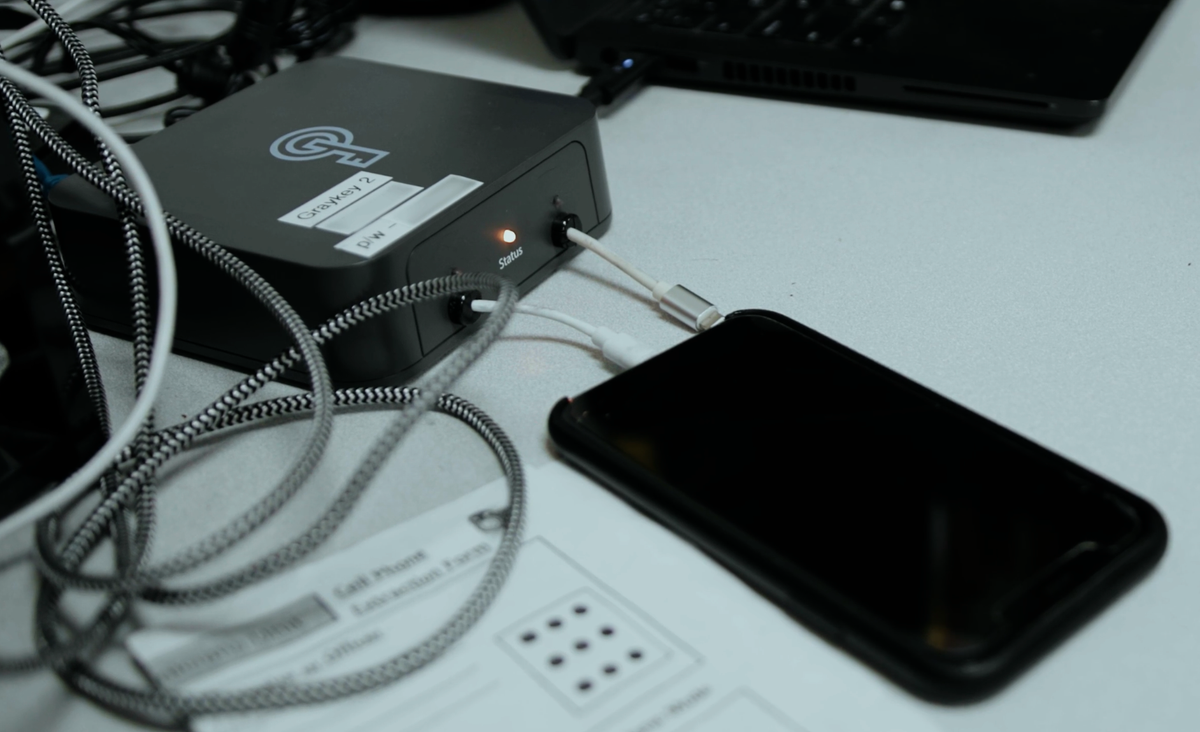
The new technology to get around inactivity reboot was developed by Magnet Forensics, the company behind GrayKey, a popular tool sold to law enforcement agencies that allows them to unlock and access data stored in iPhones and Android smartphones. Magnet has developed a new device called GrayKey Preserve and a feature for its regular GrayKey devices called Evidence Preservation Mode, according to the video.
“This is an absolute game changer for iOS forensics and a function that I wish we had years ago,” a Magnet employee says in the leaked video, specifically mentioning that the solution is targeted at the iPhone’s inactivity reboot feature and the data it makes unavailable. GrayKey Preserve and Evidence Preservation Mode are also designed to combat another iPhone feature that automatically deletes certain data — such as cached locations, and recently deleted photos and iMessages — after a certain number of days. “We’re gonna be able to preserve that data for an infinite amount of time.”
The educational and tutorial video, which was made exclusively for law enforcement agents and appears to be dated early 2025, does not explain the technical details behind this new product and feature, but gives some strong hints as to how it works. 404 Media granted the person who provided it anonymity because they were not authorized to share it with third parties.
“Now, one of the many things that the GrayKey Preserve is going to do, as part of all of this, inside of our initial access, is it’s going to enable Airplane Mode, or more specifically, it’s gonna disable our radio transmissions like Bluetooth, Wi-Fi and cellular. In doing this, that’s not only going to allow you to preserve the data in the field, but also isolate the data in the field,” the employee explains. “Even if that device doesn’t have the ability to turn on Airplane Mode or to turn off the transmitters through the Control Center of iOS. Once initial access is gained and the device is in a preserved state, we also disable all of those radios to make sure that that data cannot reach that device.”
The idea behind GrayKey Preserve and Evidence Preservation Mode is to keep the iPhone in a state known as After First Unlock, or AFU. Having an iPhone in that state essentially allows cops to access data that would otherwise be much harder to obtain if the phone was in a Before First Unlock, or BFU state. If the iPhone is in BFU, certain sensitive data is encrypted, and it can be significantly harder — sometimes even virtually impossible — to brute-force the device’s passcode and unlock it. 404 Media previously obtained lists of iPhones that GrayKey and competitor Cellebrite could access, with variations between phones in an AFU and BFU state.
“That AFU state is captured,” by GrayKey Preserve and Evidence Preservation Mode, the employee says. “Even if that device does reboot for any number of reasons, memory maintenance or the power is lost or whatever, the AFU state is not lost. This is the true magic behind the GrayKey Preserve and the Evidence Preservation Mode function.”
When using this new solution, law enforcement agents only see the iPhone’s software version and device model, rather than any data within, according to the employee and a screenshot of GrayKey’s customer interface included in the video. That allows the cops to preserve the data they care about without actually seeing it before they are authorized to do so.
Apple and Magnet did not respond to a request for comment.
404 Media shared a transcript of the video with Jiska Classen, a researcher at the Hasso Plattner Institute who studies iPhone security. While Classen said that it’s impossible to know for sure how Magnet’s new feature works based on the video, she posited some theories and agreed that it is “quite a game changer” or “at least puts things back to where they were before inactivity reboot.”
She thinks Magnet has found a way to manipulate the iPhone’s clock, effectively “slowing down time” or even “stopping the clock from ticking, even after a reboot.” Most likely, according to her, the GrayKey may disable the iPhone tasks that set data to expire.
What is certain is that the ball is now in Apple’s court to figure out how Magnet got around inactivity reboot, and find a way to prevent the company and its technology from freezing iPhones — and the sensitive data stored in them — in time.
You guys still use iPhones 😂
Judging by the value of iOS exploit bounties posted by these orgs vs the surprisingly low value for Android, they clearly have a far harder time cracking iOS devices than they do Android.
Iam on grspheneOS
That means that they believe there’s more value in having those exploits, not necessarily that they’re harder to find. Though I imagine it’s at least a little bit harder because iPhones are closed source. That does also mean that if Apple doesn’t discover the vulnerability, it’s unlikely to get a patch. With Android, these security issues are found more easily, but also patched much faster. Which I suppose makes an Android vulnerability also worth less, since you get more limited use out of it.
Is that true though? I do a lot of security work and iOS RCE vulns are typically patched same day with all devices in support getting that security patch at the same time.
Android, it’s heavily dependant on the device manufacturer etc, no? So many forks of Android plus countless handsets never get an update as they’re out of support.
And even from an OS architecture point of view, actual Android and its IPC via intents, content providers, broadcast receivers, and component exports etc is a whole world of juicy attack surface that simply doesn’t exist on iOS. Which is a primary reason people hate iOS given apps feel so isolated and you have to use the share sheet to get data between apps.
Then you have Android’s differing chipsets vs iOS’s Secure Enclave that’s on all supported handsets. Plus Android’s WebView has addJavascriptInterface() allowing native code execution via that API whereas Safari, as shit as it is, doesn’t have that enabled.
Don’t get me wrong, Android is an awesome operating system and it’s openness enables some amazing distributions like GrapheneOS.
But even a cursory glance at the two attack surfaces, iOS has a way smaller surface and swifter patching.
I do a lot of security work and iOS RCE vulns are typically patched same day with all devices in support getting that security patch at the same time.
The ones you know about, yes :). We know there are complete firms actively exploiting iOS devices though. With Android the security community can figure out what the flaws are and patch them, with iOS it’s a black box.
Android, it’s heavily dependant on the device manufacturer etc, no? So many forks of Android plus countless handsets never get an update as they’re out of support.
Most devices are legally required to get X years of security updates, and most manufacturers do push those out fairly quickly. Maybe not all the same day, sure, but they do go out.
I do remember a fair few exploits for iOS devices that allowed an attacker to take over a device without any user interaction, and most mentioned they were actively being exploited by malicious (state) actors.
All I think however is that the price of the exploit doesn’t necessarily correspond with how secure the device actually is, but rather it’s based on the value that that exploit might hold. US entities would probably also offer more than EU entities, whereas for Android it might be the other way around.
You use Android? 😂 at least graphene right? On a Google CIA sponsored phone no doubt.
You guys are using cell phones? I have a specially trained carrier pigeon that coos in AES256
256 can be decrypted by any pigeon hawk. You may as well be peacock.