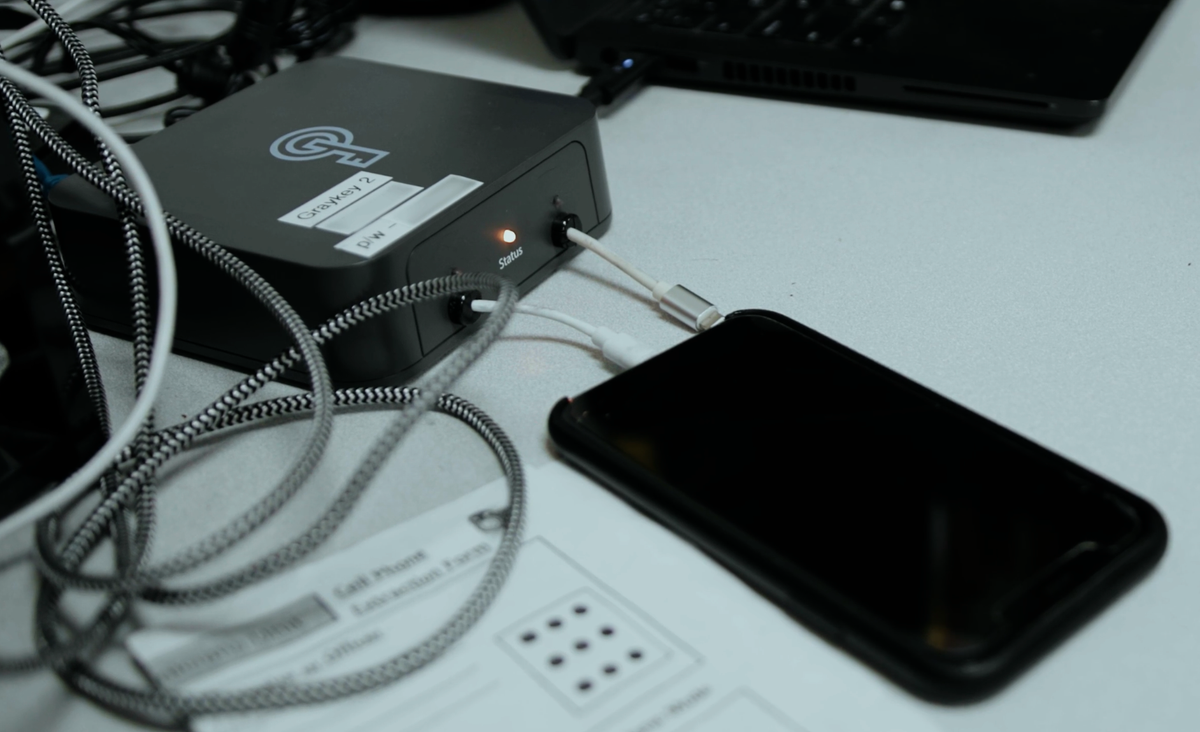
A company that makes phone hacking devices claims to have developed a solution that freezes iPhones in a state that lets cops more easily access sensitive data inside them, according to a video obtained by 404 Media.
This is the latest salvo in the never-ending battle between Apple and companies that help cops — sometimes those in authoritarian countries — break into iPhones.
In November 2024, 404 Media revealed Apple quietly introduced a new feature in iOS that automatically reboots an iPhone that has not been unlocked for 72 hours. The idea behind this so-called “inactivity reboot” is to revert the phone to a state that makes it harder for police to break into the device, and thus extract sensitive data from it with forensics technology.
At the time of Apple’s change, law enforcement agents expressed concern about this new feature, given that oftentimes they can’t immediately try to break into iPhones that have been seized. That could be because police are still waiting for a court authorization to do so, or there is simply a backlog of devices to unlock, for example.
deleted by creator
Well, I expect this to be patched asap now that it has leaked. Apple has been quick to patch things when such leaks happen. Hopefully that’s the case here too.
If only we could see what apple was doing under the hood. If only companies that constantly pat themselves on the back for being secure could be open source.
Wasn’t there a vulnerability in the chips apple uses for USB?
In the US, if cops get into a phone before a warrant, even if a warrant is issued later, all evidence from the phone is suppressed as illegally obtained.
This is a bigger concern with respect to intelligence agencies who conduct mass surveillance.
In the US, if cops get into a phone before a warrant, even if a warrant is issued later, all evidence from the phone is suppressed as illegally obtained.
This is not a hard and fast rule. There is the concept of Inevitable Discovery.
If they find evidence during an illegal entry, they may later seize it lawfully under a search warrant and prosecutors may use it in court if they can supply an independent source, rather than benefit from the earlier violation.
Real world example: In Nix v. Williams, decided in 1984, the Supreme Court considered evidence of a child’s body found after police obtained incriminating statements from Williams. Those statements were later determined to have been illegally obtained and were excluded. However, the body was located in the existing search area and the same type of location (a culvert) they were searching. It was simply in a search quadrant they had not gotten to yet. So the searchers would likely have found the body anyway even without those statements.
Well, as I’ve quickly learned, pretty much nothing in law is an absolute rule. Judges love making their exceptions.
That’s part for sure, but I’d argue that it’s more often lawmakers trying to phrase things to specifically carve out loopholes their donors want to exploit. Then judges having to work through the bullshit to determine what it actually says and whether those specific circumstances are covered.
That example I have above for instance, should the body not be admissible as evidence just because the killer told Police where it was a few hours before they would have found it anyway?
even if a warrant is issued later, all evidence from the phone is suppressed as illegally obtained.
This assumes a healthy and functioning country. I wouldn’t assume that of the US in particular. People are being hunted, kidnapped, imprisoned and murdered by the government as we speak.
I’m a law student in the US, so I’m actually privy to this information in the form of all the talks that they have judges and lawyers giving.
You may not assume that the US judiciary is healthy and functioning, but it is not as broken as most international observers (or chronically online Americans) think it is. In particular, if you have been observing the Department for Justice’s results recently, you’ll notice a few things:
- Because the Department has been hiring for loyalty and not legal skill, the Department has lost most of its prior prestige. Previously, clerking for the Department was a competitive law school position. Now, the top legal minds then to avoid it. As a result, the quality of legal skill at the Department has decreased, drastically.
- Judges in the federal judiciary, with the exception of some notable Trump cronies, is actually very willing to uphold existing procedural law and rule against the government. It happens extremely regularly.
- When judicial orders are ignored, it is almost always temporary and not in any lasting way. Federal judges still do threaten and issue contempt of court penalties and disciplinary referrals to officials who blatantly disobey court orders.
So in short, you are partially correct and partially wrong. The judiciary of the US has shown to be remarkably resilient considering it has withstood two years of a fascist in power and in full control of the legislature.
Federal judges still do threaten and issue contempt of court penalties and disciplinary referrals to officials who blatantly disobey court orders.
I guess this is my main point of concern right now, as an outsider. I know that the courts are still ruling against Trump and the Republicans fairly regularly, but then I hear about situations where they’re simply ignoring the courts’ rulings and little seems to actually happen as a result.
What do those “disciplinary referrals” actually do? Do people actually get fired, or is it just something else for the Republicans to ignore?
Disciplinary referrals are issued against lawyers who break the court rules. Contempt of court is used against anyone (lawyer or not) who violates a direct order from the court. A lawyer who blatantly violates an order may receive both a disciplinary referral and also a contempt of court penalty.
Before a court issues a penalty of any kind against anyone, they usually issue what is called an order to show cause, which essentially means the party accused of violating the rules must appear before the judge and explain why they should not receive a penalty.
Disciplinary referrals are addressed to the state bar association, which are organisations comparable to guilds which license lawyers. The bar association can impose penalties against the lawyer which include:
- Censure, a formal finger-wagging which leaves a permanent mark on their licence and is generally considered detrimental to future job prospects
- Mandatory ethics training or re-take bar exam
- Temporary suspension of their licence to practise law
- Disbarment and expulsion from the bar association, which permanently revokes the lawyer’s licence to practise law. This typically cascades to all bar associations across the country.
An example: Rudy Guiliani was a Trump lawyer who filed submissions before several courts containing information he knew to be false and raising allegations he knew were unsubstantiated, as a part of Trump’s scheme to overturn the 2020 presidential election. The New York bar association disbarred him for this, and the DC bar association took note and automatically disbarred him as well. His legal career is finished; he cannot legally be employed as a lawyer anywhere in the country.
Contempt of court is an inherent power of the court to punish people who violate its orders. A judge can, on their own initiative, declare someone guilty of contempt of court and impose a punishment for it, which could include:
- A fine, possibly an increasing fine until the order is complied with. The fine is paid personally by the person found guilty of contempt of court and no immunities apply.
- Imprisonment for a fixed term, usually not more than a month
- Imprisonment until the person complies with the order
- Anything else the judge comes up with, that does not violate Amendment 8 of the US Constitution or relevant laws
Example: A lawyer was fined $10,000 in March 2026 by my state’s Court of Appeal for submitting a brief containing AI hallucinations.
Ah, so as this progresses the Republicans steadily run out of “competent” lawyers because they keep getting disbarred (or quitting to save their legal skins), leaving them with increasingly incompetent ones that have an even harder time accomplishing stuff.
Here’s hoping their legal wells run dry quickly, I suppose.
they will have to keep sourcing them from legit law firms, but law firms require them to disassociate from the firm before working for someone like trump or gop.
Remember in the early days of Trump II when we were hearing about entire US Attorney’s offices quitting in protest? That no longer happens, but that’s what happens when top brass asks experienced, career lawyers to defend positions they know are indefensible, and insists they sign their name to hot garbage, that they know is the same kind as what got Rudy Guiliani disbarred.
So yes, the Trump Justice Department is indeed running out of good lawyers and that’s why the US Attorney’s Office for DC is led by a Fox News commentator who happens to have a law degree.
jeannie piero, the drunk lawyer.
The judiciary really needs to start using “Imprisonment until the person complies with the order” a lot more early, often, and against people higher up in the DoJ org chart.
First of all, you’re doing important work and I wish you well in your studies and career, for everyone’s sake.
Thanks for the insight. Definitely some positives there. When ICE have added an innocent person’s data to be absorbed into (eg) Palantir’s database, how confident can we be that it is actually removed again?
If this is illegal (which I am not convinced that it is, even though it certainly should be), then a judge can order Palantir or the relevant government agencies to destroy the data. If there is a question about whether this order will be complied with, the court can appoint a special master to oversee it, but this is rare. Usually what happens is the court will take their word on it, but if it turns out they lied, then the court will impose a stiff penalty for contempt of court.
Yep, and the concern shouldn’t just be for yourself - authorities will clone the phones and then comb your contacts and social media and then add to their systems compiling relational data and use that to target people, often innocent people. Your phone data won’t just be used to harass or inconvenience or stress you out, it’ll be used to harm other people. You should care about that.
So, y’all gonna switch to GrapheneOS now?
The companies who sell these bypass devices spend time on graphene too, don’t worry.
The price of iOS exploits would suggest Apple’s doing a pretty good job in this area.
I’m sure they do spend time on Graphene OS, but that’s not the same as being successful in cracking it.
I wonder if they spend time on Linux mobile devices, considering how niche they are.
But then again, security through obscurity is not real security, and I’m not aware of any reasonable way to run something like QubesOS on a phone in any way that would be usable.
An apple user using graphene?
You are a funny person.
Does graphite disable faceid and touchid?
On Graphene, Lockdown mode disables biometric login until you unlock it manually with your passcode, but the device is still in the less secure AFU (After First Unlock) state.
You can also set it to restart the device if not used within a set time period. Various settings from 10 minutes to 72 hours. So if you haven’t touched your device within that time period, it will shutdown and restart, going back to the more secure BFU (Before First Unlock) state.
Lost mode, already there and sold…
It’s almost like there’s only two ways to actually accomplish this type of thing. You can do the same basic thing but use different names to differentiate where/how that function is used.
Lock it and require the passcode where the decryption key is still in memory because the system is running, or shutdown/restart the device so the decryption key isn’t in memory anymore.
What would a third option even look like?
Are you. Understanding a standard shut down does what you want? It’s the most basic function of a device. On off, if you don’t know it. You shouldn’t use the device . In fact I’d call you massively stupid for not learning how when you bought it
Are you. Understanding a standard shut down does what you want?
What are you babbling about? Of course, that’s why I already said it. Twice.
Both comments I have made in thi thread have mentioned shutting down or restarting the device to put it back into a BFU state.
Since you clearly didn’t actually read the comments you are replying to… I’ll include the relevant parts from both below:
You can also set it to restart the device if not used within a set time period. Various settings from 10 minutes to 72 hours. So if you haven’t touched your device within that time period, it will shutdown and restart, going back to the more secure BFU (Before First Unlock) state.
Lock it and require the passcode where the decryption key is still in memory because the system is running, or shutdown/restart the device so the decryption key isn’t in memory anymore.
You still didn’t answer the question I posed though… before replying in way that seems to indicate you either can’t, or refuse to actually read before responding condescendingly.
Since you seem to think there should be another choice instead of doing the same two things to protect the device/data… what would a third option look like? Other than locking and disabling biometrics, or a shutdown/restart putting the device back into BFU mode.
Or are you just stuck thinking a shutdown and reboot are technically different things? Even though that makes no difference here since they both put a device into BFU.
You can disable. You can also two factor it e.g. fingerprint and pin, with also a long password for BFU.
The fingerprint is the way in they are using. Bio entries are owned by the police if arrested. Finger/face/eye. Passwords/passcodes are not.
(Basically they own your body, not your mind without a warrant)
They are not supposed to own my body except as a punishment for crime whereof the party shall have been duly convicted.
/hj
Fingerprint and face is allowed under most states
Yeah, I was making a 13th Amendment ‘joke’, since you said “own”
Lockdown mode disables biometrics while still leaving your device on, say if you know you’re going to talk to the police and don’t want to be forced to provide biometrics to unlock the device. And you can setup an automatic reboot after a set time period where it would return to a BFU state automatically.
So it’s a mimic of lost mode with no new features?
Bring back the power hard switch. Problem solved.
And a removable battery. One I can guarantee the battery will pop off if I accidentally drop it while my hands are in the air.
The government can do anything they want to you. We are cattle.
If Apple really cared, they would make it so that a Shortcut that performed the Reboot action was allowed to run on a schedule, unattended. But no, that’s specifically disallowed.
I assume that would just be shutting down the phone. When it boots up it required the passcode, which is what they want to bypass here
No, this preserves the phone in an “after first unlock” state. They specifically dont want a phone to reboot or shutdown because then the encryption keys get dumped from memory and require the password to decrypt the keys.
Yeah… Aka if it was shutdown. It isn’t before first unlock state. So if you are going to get arrested, shutting the phone off mitigates all of this
Disclaimer: I only use iPhones for security testing, so this is more from related literature rather than first-hand experience.
IIRC the hardening unattended reboot could offer is already covered better by options like disabling biometric unlock, security key 2FA, enabling lockdown mode, enabling advanced data protection, disabling iCloud, disabling USB accessories, and so forth. Also unattended reboot seems like an easy prank vector or foot gun to render a device permanently inaccessible (i.e., device always reboots immediately after pin entry) requiring recovery mode reset or restore to fix.
A. If you want 2fa to unlock a phone fuck off B. One has to opt in to iCloud. (It’s way to fucking motivated and absolutely a forced thing in my opinion though)
If you can’t download an app without being signed into an account… You paved the way for Microsoft. Literally were the worst of the worst and made it so. Even the Microsoft store allowed $0 purchase without sign in for years after if not possibly still today. (I don’t use them).
That said… Security testing anything should tell you the Apple/Google/Microsoft system is all wayyyy more secure using 2FA and activation locks we all hate because theft is a thing. We shouldn’t need an original proof of purchase to unlock a device, yet we do because social engineering makes it that way.
Agreed, I’m pretty used to security key unlocks and still wouldn’t want that friction on a personal device.
Also just for completeness, since I forgot to mention: enabling stolen device protection and findmy/mdm to enable remote wipe.
Yeah, a security key for Apple disables you ability to receive the account with them.
Most smartphones encrypt the majority of their storage these days.
This means there are two states the phone can be in.
BFU, or Before First Unlock, is the most secure. When you power on the phone it has just enough software in unencrypted storage to come on, initialize its hardware, start some background processes, and display an unlock screen. This is the most secure state for the phone. When you type in your password, the password itself decrypts the actual key which is used to decrypt the main storage. Without that password, the data is essentially useless as it cannot be decrypted. Also, most phones are now set up so that if you try the wrong password 10 times, it will erase the main storage encryption key which means the data is completely unrecoverable forever. In general, it doesn’t matter what you can exploit BFU because there’s very little running to exploit and the storage encryption key is usually stored in a secure enclave, that is a special part of a chip that is designed to resist tampering.
Once you type in your password the first time, the phone is AFU, or After First Unlock. The key to access main storage is held in memory, it is being actively used to read and write from that storage as software is running on the phone like email, background apps, etc. The prompt to unlock the phone looks exactly the same, but in reality the phone is in a much less secure state. There’s plenty of software, both system and apps, running for you to try to exploit.
The point here is that if you set the phone to regularly reboot, or to reboot if you haven’t logged in in a day or two, each time it reboots it switches back to BFU state.
And so if some government agency has arrested you and seized your phone, you want that reboot to happen because if the phone automatically reboots before they manage to get into it, it becomes much much harder for them to get in.
Shhh… you’ll piss off the people that don’t like to hear they are ignoring all vulnerabilities that we protected by such. Near 99% of people are ignorant of how access works to an account, and how it should be secured. Anyone who complains about 2FA is normally a dumbass
I don’t have a phone.
So you dont play Diablo?
Never met the guy.
Yes you do